Hawk Code
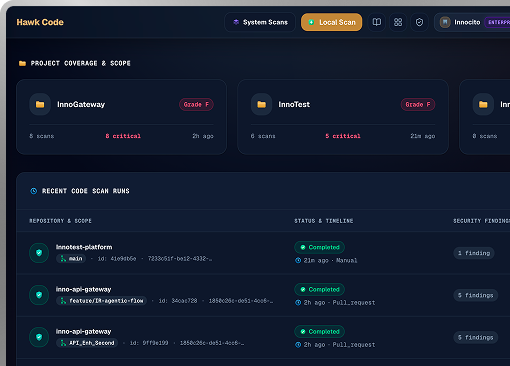
Point it at a GitHub repo or a local codebase, no source-control access needed. It covers static analysis with first-party taint tracking that follows user input across functions to dangerous sinks, dependency and container CVEs, secrets, infrastructure-as-code and CI/CD, with reachability to rank what's genuinely exploitable. A live advisory feed shows which of your repositories a new vulnerability affects, with a verified fix a click away.
- SAST
- SCA
- Secrets
- IaC